Cert-level IT. For every organization.
It's not what we do. It's how we do it. Our own software ties together your help desk, onboarding and offboarding, laptops and phones, email, Wi-Fi, backups, passwords and every SaaS app you run, as one automated process, checked every day. So your IT comes out defensible with SOC 2 and ISO 27001 best practice.
No other IT company does what we do. We built the software that makes it possible.
Check your company for security vulnerabilities
Free, about a minute, no commitments.
Every change approved by a person on our team
22 of 23
Organizations we checked had at least one public vulnerability
19 of 23
had email anyone could fake in their name
5.0
from 123 Google reviews
1 bill
IT and security together, no surprise invoices
Other IT companies run your IT from spreadsheets. We run it from software you can see.
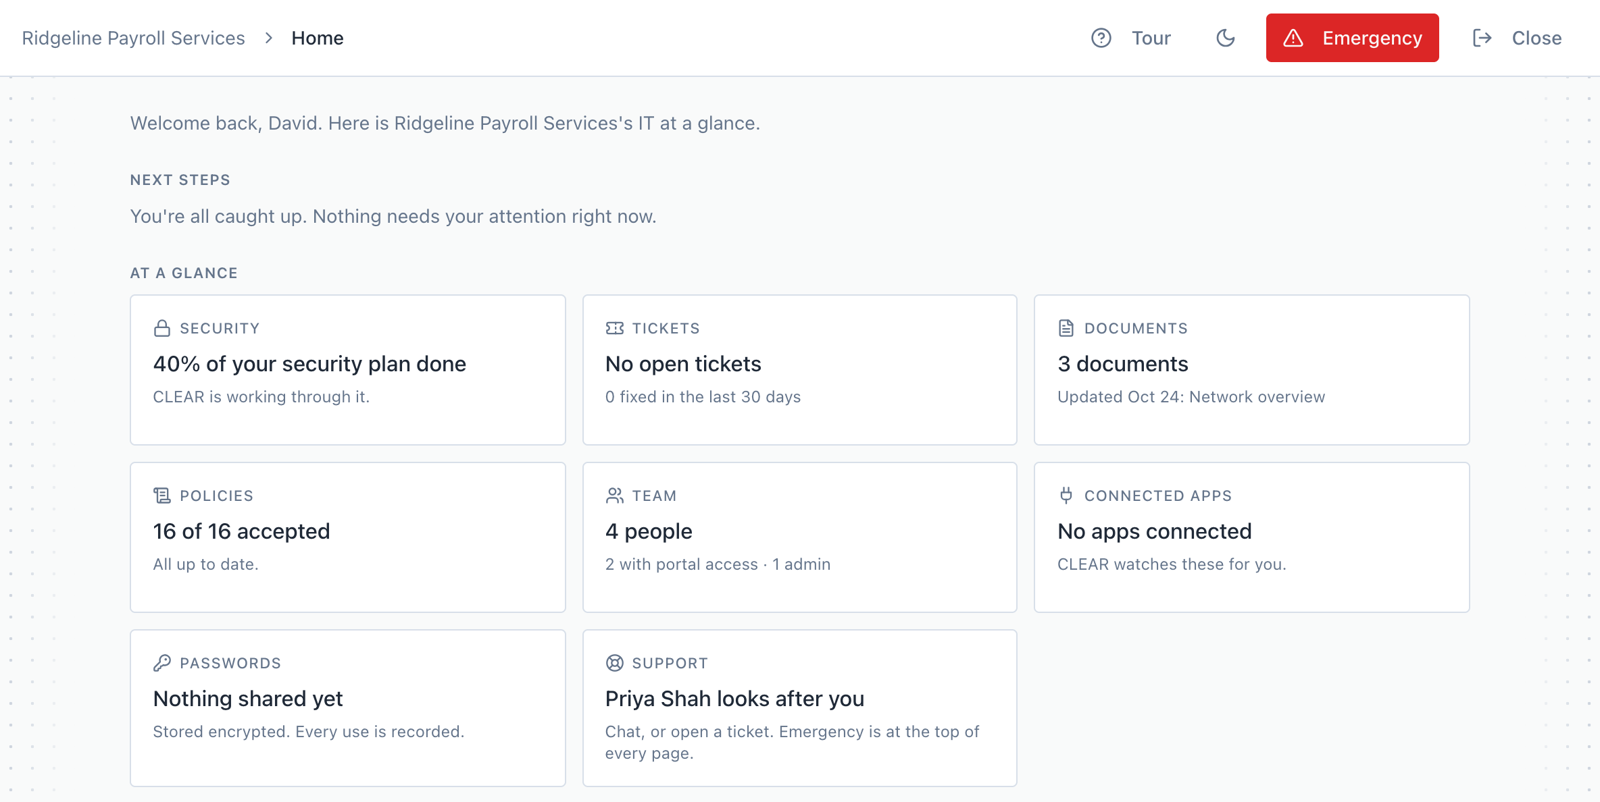
Most IT companies try to keep things organized too. They use spreadsheets, or off-the-shelf tools that only hold what someone types in. Neither one connects to your accounts, talks to anything else, or checks anything on its own. They're only as good as the last time someone remembered to update them. We built software instead. It connects to Google, Microsoft and every app you run, and checks every account and setting every day. You see all of it in your portal, any time.
Every one of those runs through our security guide. That's why your everyday IT lines up with what SOC 2 and ISO 27001 auditors check.
Everything looked fine. Here's what was actually open.
01
The account nobody closed
A bookkeeper left in March, and her email was turned off the same day. She still had a login to the payroll app, set up two years ago with her personal email, and nobody knew it existed.
Our software keeps a list of every account in every app you run, so it flags hers right away and someone on our team closes it.
02
The quiet forwarding rule
One mailbox sends a copy of every email with "invoice" in it to an outside address. Whoever got into that account months ago set it up. Email still works, so nobody notices.
Our software checks every mailbox's rules every day and flags any that send mail outside your organization.
03
The one admin without two-step sign-in
Two-step sign-in is on for everyone except one admin account an old vendor set up for a project. It's the one account that can change everything.
Our software checks every account, including the forgotten ones, and keeps flagging it until it's fixed.
Examples, not real clients. They're the kinds of gaps we find most often.
Three companies, three bills, and the vulnerabilities fall between them.
Most organizations pay an IT company, then a security firm when an insurer or a big customer asks hard questions, then audit prep if they ever want a certificate. Nobody owns the whole picture.
The IT company
Fixes what breaks. Rarely checks the settings that don't break until the day they do.
The compliance tool
Hands you a checklist and a passive dashboard. The work is still yours.
The security firm
A report once a year, then gone. The findings sit in a PDF.
You
Three invoices, and a former employee who can still access company email and files.
No other IT company does what we do. We built the software that makes it possible.
One service that does what the IT company, the security firm and the audit prep each do. IT and certification-level security in one, automated and defensible.
* Except the controls for writing software, which only apply if you build software.
CLEAR 2026:55. The new IT standard.
Because every client runs through the security guide, your IT meets 55 controls covering both halves of what auditors check: the settings, and the program around them. Every SOC 2 and ISO 27001 requirement maps in automatically, so you can show an insurer, a customer, an investor or an auditor exactly where you stand.
Who controls your domain, your DNS records, your website's secure connection
Admin access, fake email blocked, hidden forwarding rules
Your shared drives, and who can open what
Your office network, Wi-Fi, web filtering, safe remote access
Password manager, strong passwords, two-step sign-in for everyone
Encryption, device management, threat protection, wiping old devices
Alerts, logs kept, updates on schedule, known holes patched
Locked equipment, cameras where they matter, fire and power, visitors
A real backup, tested restores, a plan for getting back to work
Training, practice phishing, offboarding, background checks
How staff report it, the response plan, written policies, roles
Every app you pay for, who has access, how safe your vendors are
The rules that apply to you, personal data, breach notices
Two-person approval for payments, a yearly review you sign
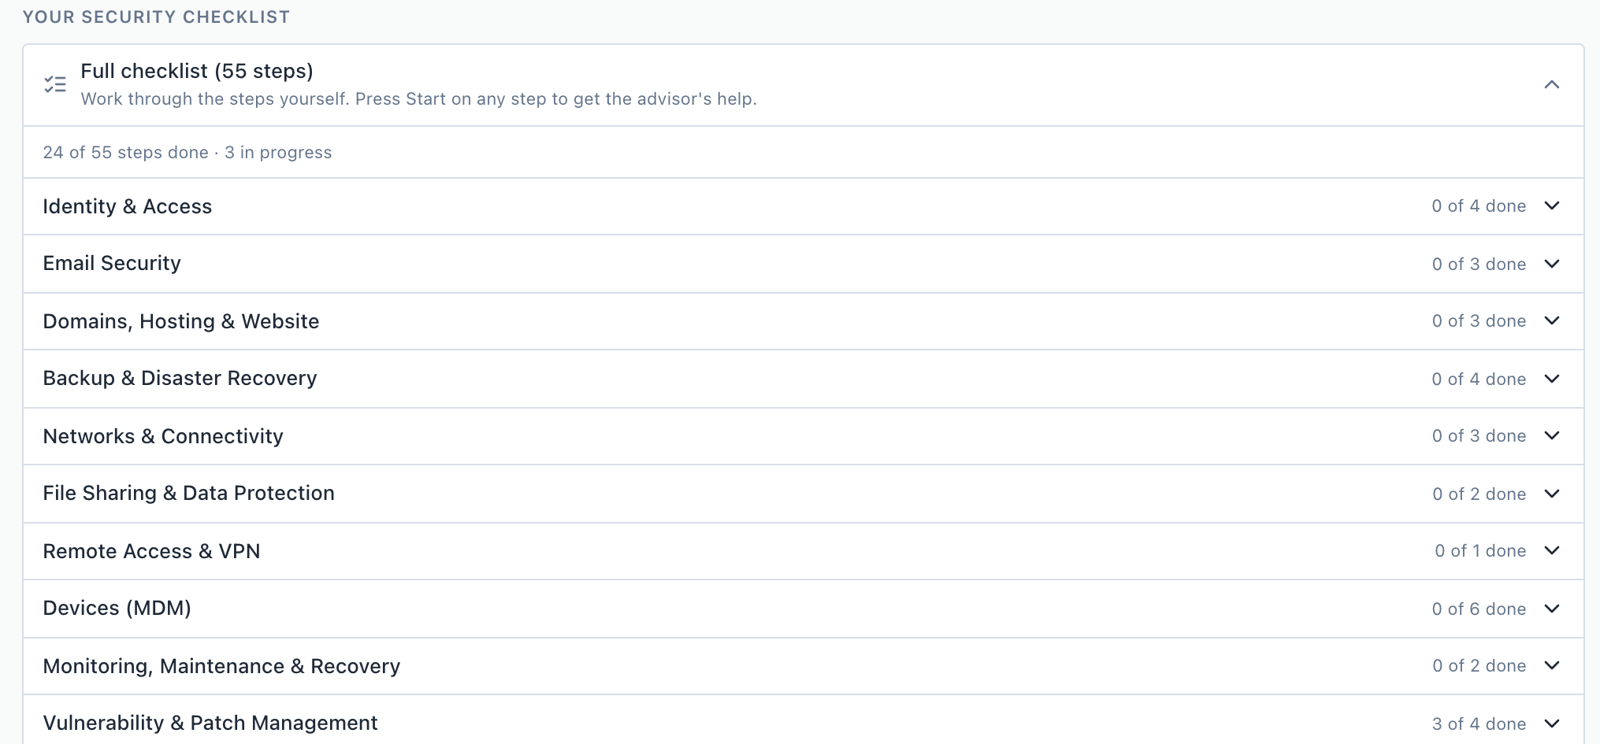
Your checklist, by area, in your portal
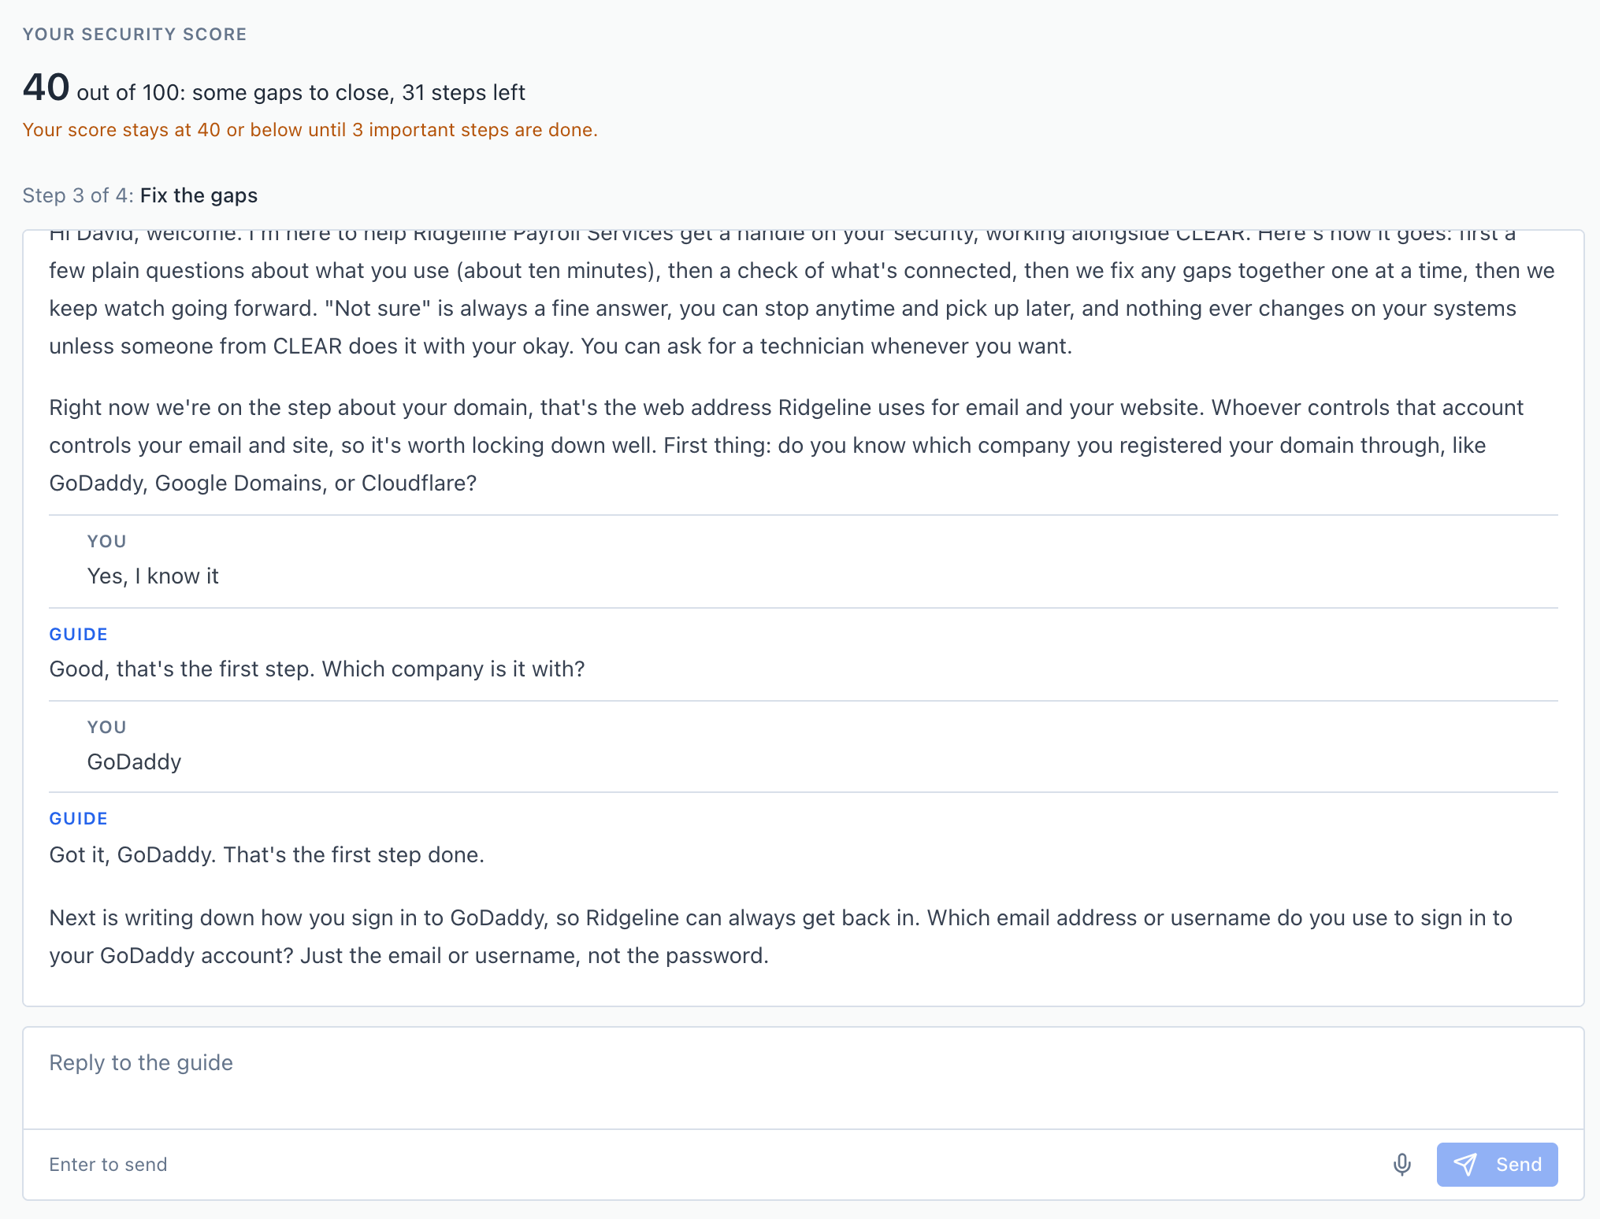
Security guide
Does everyone on your team sign in with a second step, like a code on their phone?
The guide automates each step in plain English
CLEAR 2026:55 is our own standard. Only an audit firm can issue a SOC 2 report, and only an accredited body can certify you for ISO 27001. What you get from us is everything those audits check, with the evidence behind each item. If you decide to get certified, your auditor starts from our record instead of a blank page.
Not just software
Software automates.
A person approves.
"All organizations deserve the security big companies pay auditors for. That's how we manage your IT, every day."
Matt Moglia, owner, CLEAR Technology
01
Check
Type your website address. In about a minute you see what anyone on the internet can see about you.
02
Fix two, free
We fix the two biggest problems the check found, this week. No contract.
03
We take over your IT
Help desk, accounts and devices move to us, and we close every gap in CLEAR 2026:55, one by one, in your portal.
04
Stay there
Our software checks every day. We find and close gaps, and every one is auditable and defensible.
5.0 from 123 Google reviews. Read every one, unfiltered.
Start with two free fixes. Experience the CLEAR difference firsthand.
What day and time over the next couple of weeks works to share a coffee on Zoom and go over your setup together?
Check your company now
The two worst problems fixed this week
Up to two hours of work, about $440 at our regular rate, free. No contract.
No platform or per-user fees for your first three months
If you'd like us to keep going after the fixes, your monthly platform and per-user fees are waived for your first three months. Hourly work beyond the two free fixes is billed at our regular rate.
Every control decided within 90 days, or your fees stay waived
Within 90 days of starting, every control in your plan is in place, or marked not applicable or risk accepted with your signature. Otherwise your monthly platform and per-user fees stay waived until it is.
3 new organizations a month
We bring on 3 new organizations a month. Lock in your spot.
After the first three months it's month to month, with 30 days' notice to stop.
Common questions. Ask us anything else on the call.
Your everyday IT: the help desk, setting up new staff and closing out departing staff, laptops and phones, accounts, email, Wi-Fi and the apps you pay for. Then we add what other IT companies can't. Our own software connects to Google or Microsoft and every app you run, keeps a live record of every account, device and setting, and checks all of it every day against CLEAR 2026:55, our security standard. When something slips, like a departed employee's account left on or two-step sign-in turned off, it gets flagged and fixed. You see all of it in your portal: your tickets, your documentation, your checklist and your progress.